CyberCaddy works as the security team for Australian IT leaders. We've deployed and run security platforms across many client environments, and we take on the monitoring, testing, consulting and compliance work your team doesn't have time for.

Trusted by 80+ Australian organisations
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
Four reasons IT leaders choose CyberCaddy.
Monitoring, testing, consulting and compliance, delivered by one team that knows your environment.
.png)
24/7 monitoring, detection and incident response through the MDR partner that suits your environment, managed by CyberCaddy.
Learn more →
Cyber reviews, vCISO and incident response planning, from a one-off review to ongoing strategic advice.
Learn more →.png)
Real-world attack scenarios that find the weaknesses in your environment before an attacker does.
Learn more →
Essential Eight, ISO 27001, SMB1001 and SOC 2, built around how your organisation actually works.
Learn more →.png)
Protecting operational technology and industrial control systems from cyber threats specific to physical infrastructure.
Learn more →%20(8).png)
Find and govern the AI tools your people use, with AIDR from Field Effect, delivered and managed by CyberCaddy.
Learn more →We engaged CyberCaddy for both their Managed Security Operations and Cyber Consulting, and the comprehensive value has exceeded our expectations. I'd highly recommend them to anyone looking for a dependable and well-rounded cyber security partner.
Before CyberCaddy, our digital security was a blind spot. They didn't just provide a service — they built a culture of resilience within our firm. Now I have total confidence our operations are protected.
Their structured approach gave us clarity, confidence, and a strong foundation for ongoing security. Through their vCISO service, they implemented key policies and aligned our practices with a recognised framework.
Platforms we work with
We work with multiple security vendors, including several MDR providers, and recommend the one that fits your environment.

.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
.png)
Most IT leaders we speak with aren't starting from zero. They have tools, an IT provider and often an MDR service. What's usually missing is someone with the time and depth to check whether it all works together.
Who chose it, and is it tuned to your environment or running on default detections? An alert only helps if someone acts on it.
EDR covers one layer. It doesn't see misconfigured cloud storage, over-privileged service accounts, or a vendor with legitimate access that's been compromised.
At what maturity level, and assessed by whom? A Maturity Level 1 self-assessment and an independently verified Maturity Level 2 are very different positions.

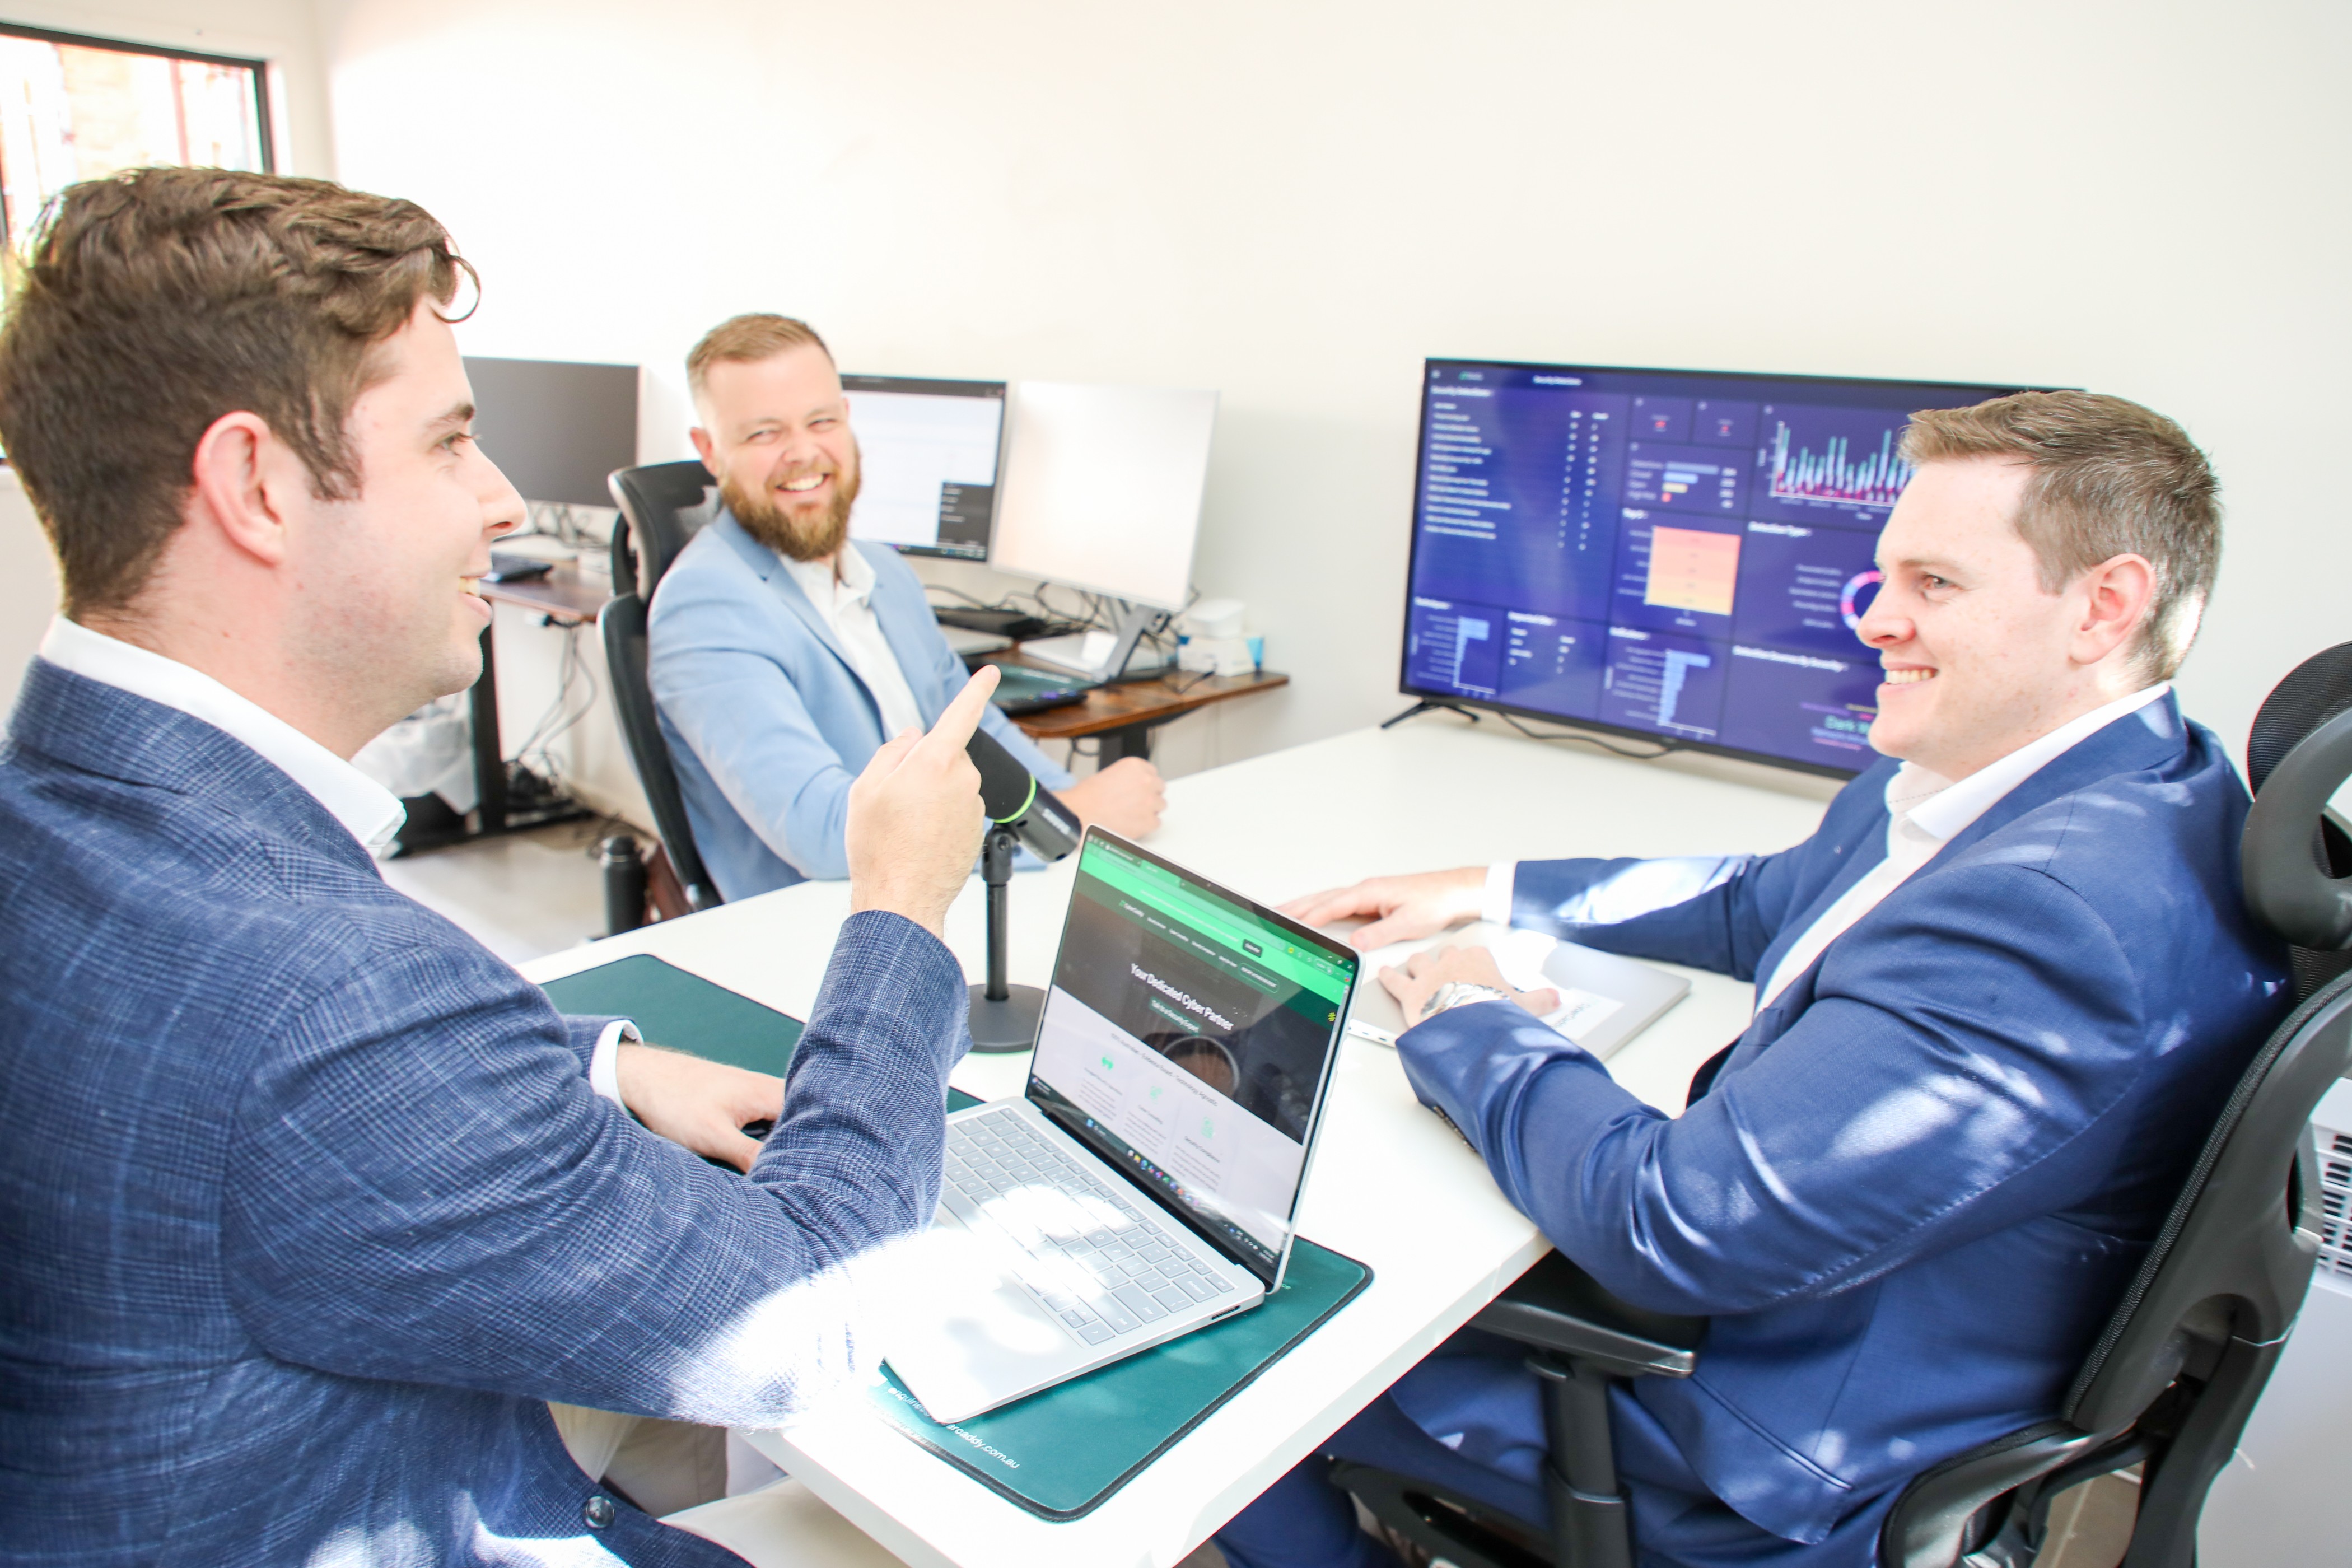
Three founders with 35+ years of combined security experience. Every engagement should leave the client's team more capable and more in control than when we started.
Meet the team →Free Playbook
Grab the AI Governance Playbook
How to adopt AI safely in 2026 — the visibility, controls, and 5-control policy framework, in 15 practical pages.
Get the playbook →